Secure every request
Verify every request
Verify every request across services and environments
Modern AI systems span services, agents, and infrastructure layers. Security cannot rely on assumptions—especially internal trust. In connected environments, one compromised component can put the entire system at risk.
Security is not layered on top. It is foundational.
Secure without assumptions
swarmd.ai is built on a zero-trust architecture that verifies every request, including those between internal components.
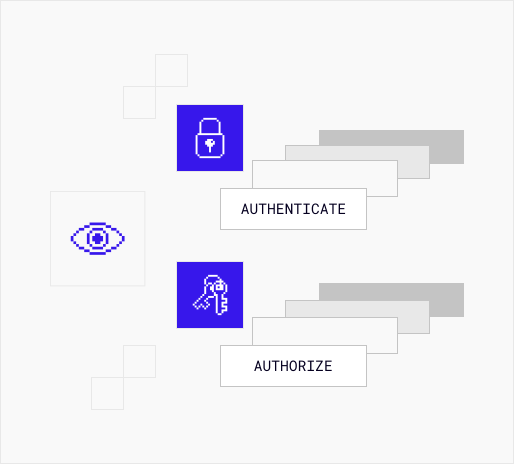
No service is implicitly trusted. Every interaction is authenticated, authorized, and validated before execution.
How it works
Verify with zero trust
Every request — internal or external — must be explicitly verified. Services do not trust each other by default. Authentication and authorization are enforced continuously.
This reduces lateral movement, limits blast radius, and strengthens internal controls.
Deploy in air-gapped environments
swarmed.ai can operate in fully isolated environments without internet connectivity. This enables secure deployment for military, government, and highly sensitive infrastructure use cases.
The system remains fully functional while completely disconnected from external networks.
Run on any infrastructure
swarmed.ai supports flexible deployment across cloud, multi-cloud, hybrid, and fully on-prem environments. You are not locked into AWS, Google Cloud, or any single vendor.
This is critical for banks, defense organizations, and enterprises operating across multiple regions and compliance zones.
Why this matters for your team
Without swarmd.ai
- Implicit internal trust
- Cloud vendor lock-in
- Limited deployment flexibility
- No air-gapped operation
- Higher lateral movement risk
With swarmd.ai
- Zero-trust verification for every request
- Air-gapped capable deployments
- Multi-cloud and on-prem flexibility
- Isolated and sovereign infrastructure options
- Reduced attack surface